Tableau Testing – Security
Security Testing for Tableau
Automate security testing across your Tableau content so the right user always sees the right data, and you can prove it. Row-level security validated by simulation, not by assumption.
Trusted by more than 600 leading companies and organizations
Seven BI testing dimensions – Wiiisdom for Tableau
What it does
Configured once is not verified.
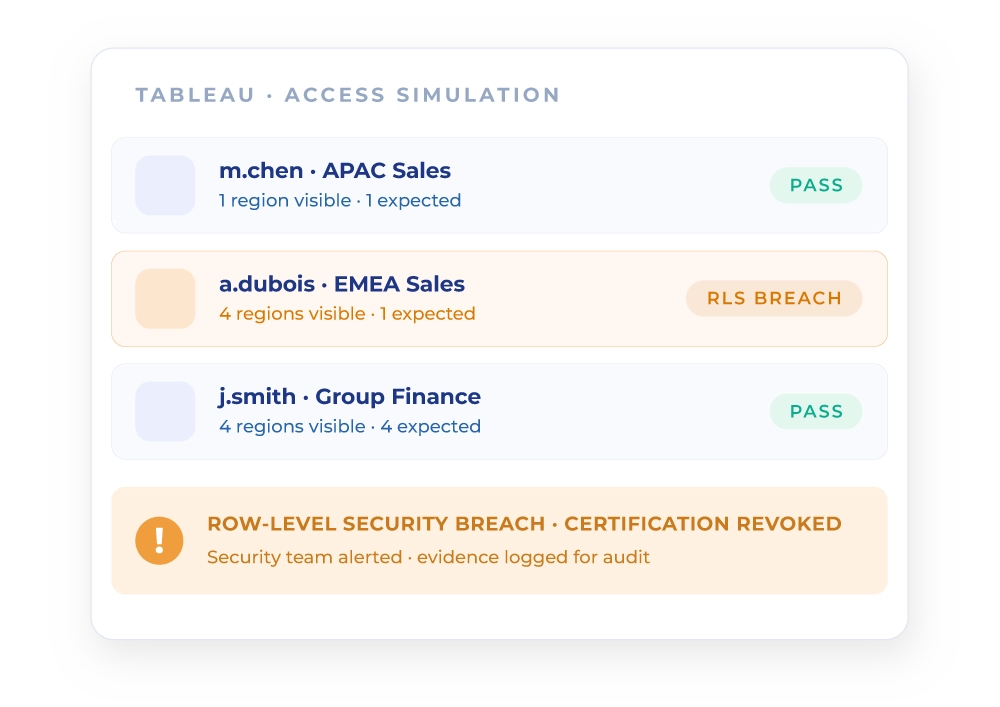
Validate row-level security by simulating real users
Row-level security is configured once and trusted forever, which is precisely the problem. Wiiisdom simulates a given user and visually confirms what data is actually accessible inside a dashboard. Restrictions are verified against reality rather than against intent, so confidentiality holds after every change to content, permissions, or the underlying model.
Protect data access at scale
Permissions drift as content proliferates: workbooks get duplicated, data sources get reused, groups get restructured. Automated security testing runs across your critical Tableau assets continuously, catching exposure the moment it appears instead of at the next annual review.
Comply, and document the proof
Meet your data security policies with test results that are captured, timestamped, and attributed, with support for GDPR, HIPAA, GxP, and SOX requirements. Audits become a retrieval exercise rather than a reconstruction project.
Keep AI inside the same boundaries New
Tableau agents, Pulse, and external LLMs consume the same content your users do. Validating security on that content is what keeps AI-generated answers from surfacing data the requester was never entitled to see.
Key capabilities
No code. Verified by simulation.
The payoff
From configured once to verified continuously.
Row-level security is configured once and trusted forever, which is precisely the problem. Wiiisdom verifies what each user actually sees, continuously, and produces the evidence an auditor will ask for.
- Row-level security is set up once and assumed to hold
- Nothing errors when a filter stops restricting; the dashboard just shows more
- Permission drift follows every duplication, reuse, and group restructure
- Exposure is discovered at the annual review, or by the wrong person
- Access verified by simulating real users and reading what actually renders
- Several personas tested against the same asset, continuously
- Drift caught the moment it appears, not at the next review cycle
- A failed check raises an alert immediately, and the exposed asset can be moved to a secured location
Agentic analytics governance
Accuracy is one of seven BI testing dimensions.
Testing is the foundation. It powers the three capabilities of the Wiiisdom platform.

Keep exploring